Findings that stand up to scrutiny.
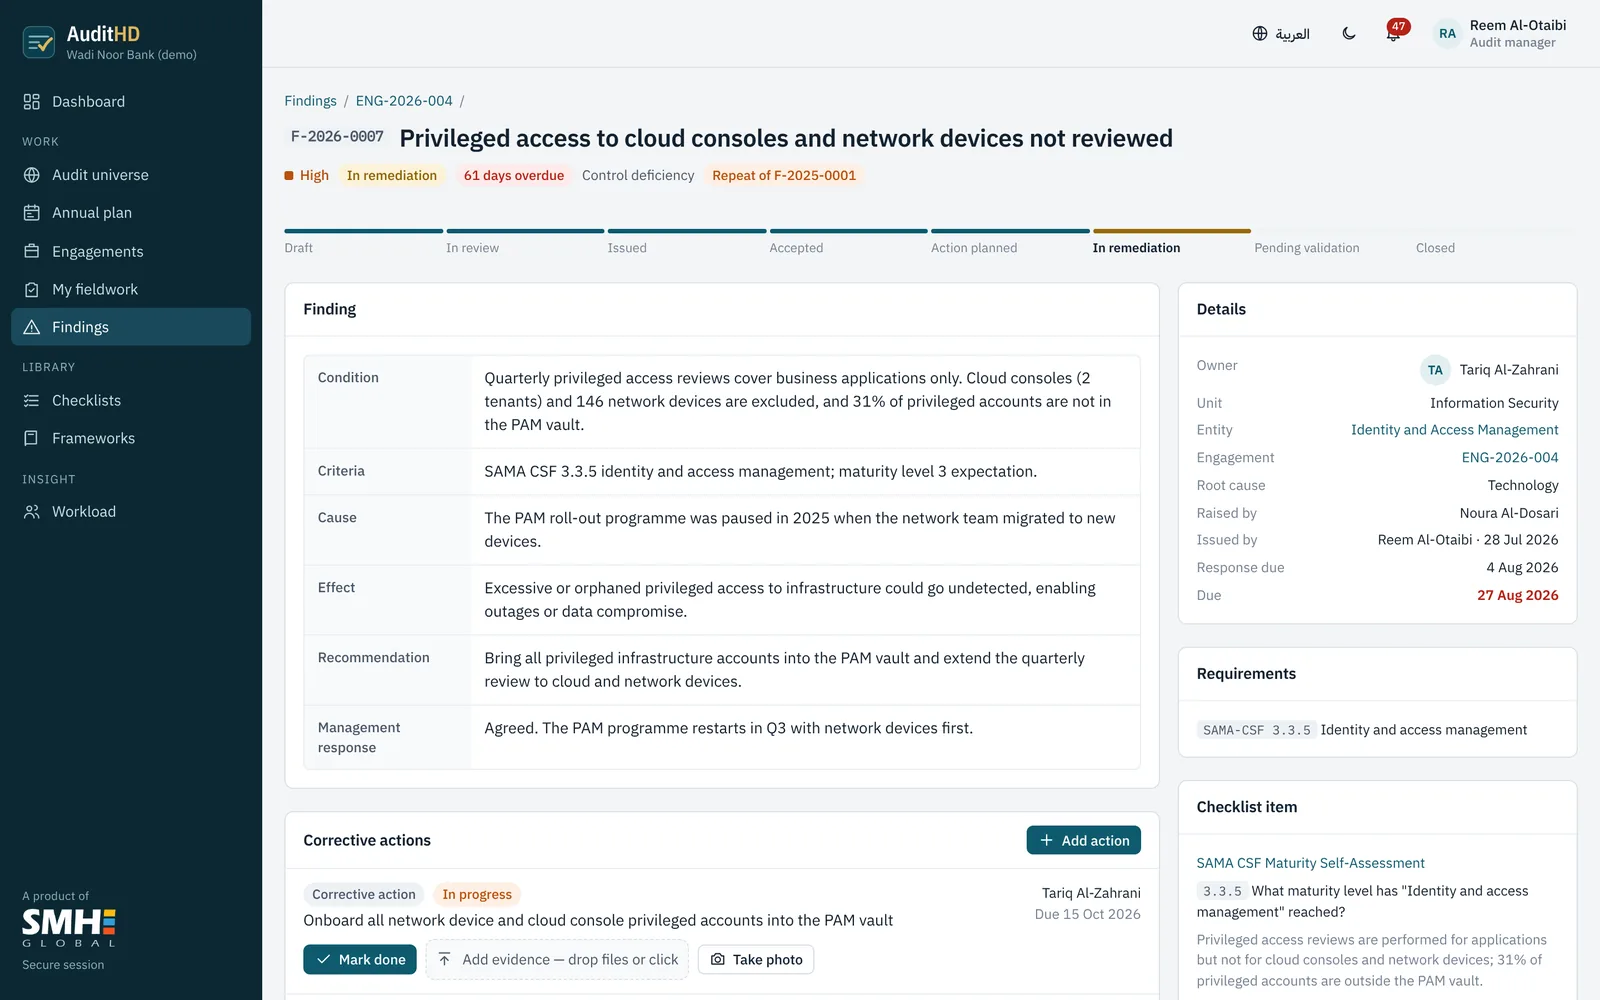
Every finding has a condition, criteria, cause, effect and recommendation, links to the clause and the evidence, and passes through review before the auditee sees it.
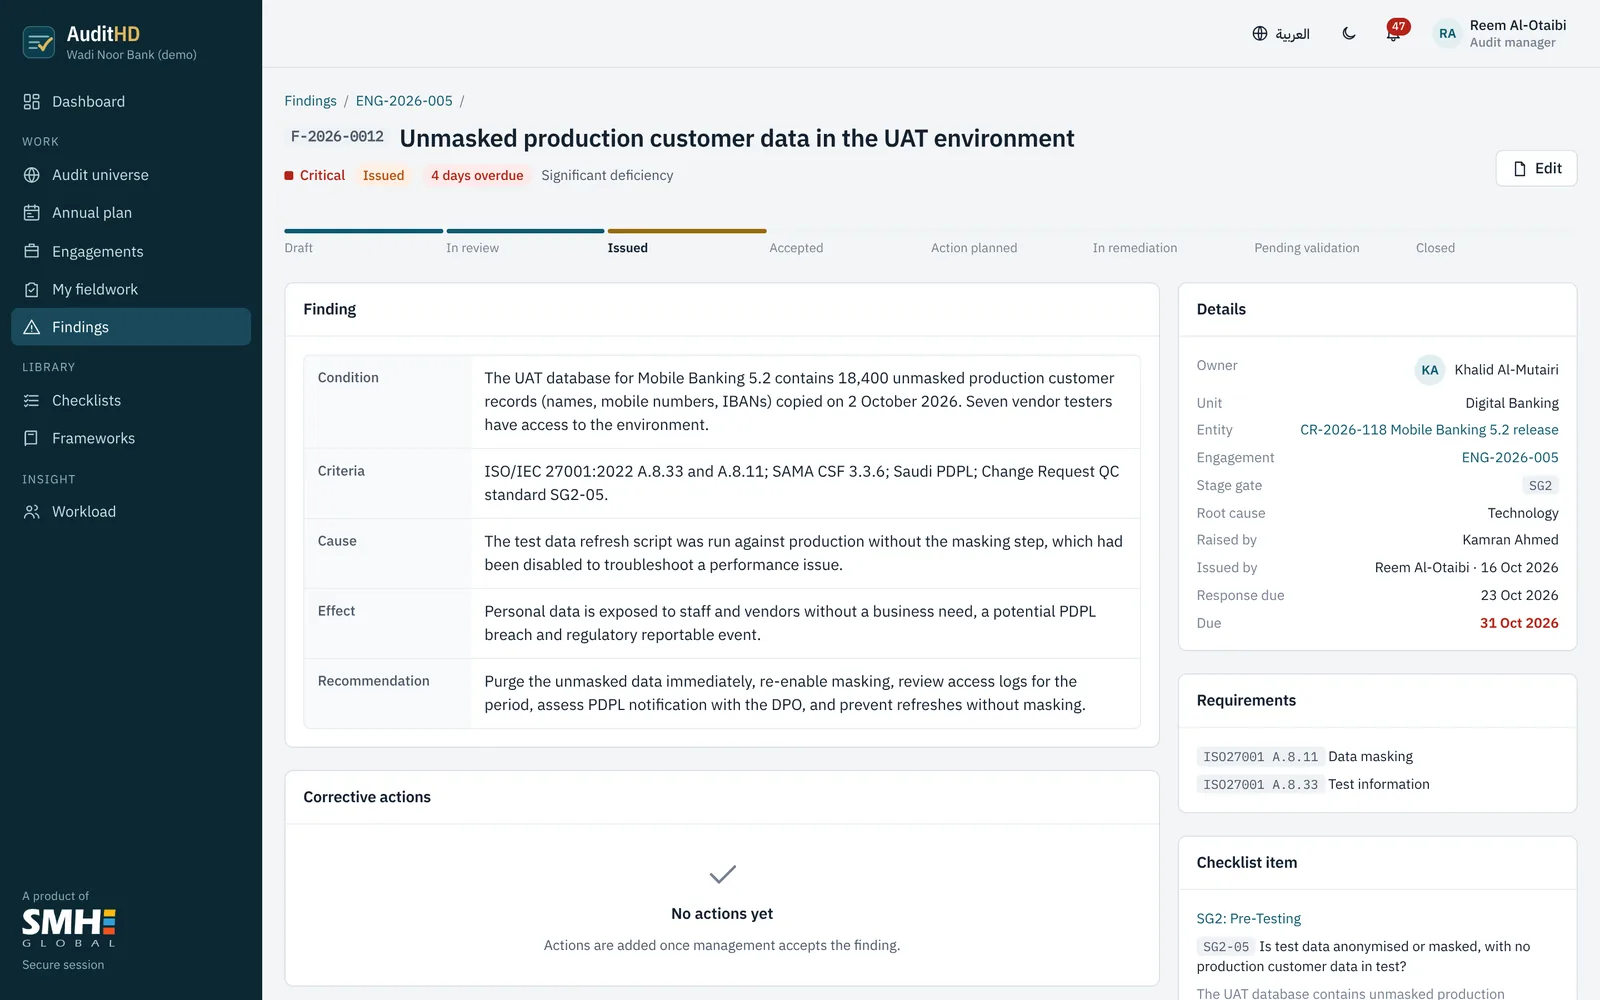
A lifecycle with checks at every step.
Draft, in review, issued, accepted or disputed, action planned, in remediation, pending validation, closed. Risk acceptance and withdrawal are recorded with reasons.
Maker-checker
The auditor who raised a finding cannot issue it; a manager or reviewer must. The owner of an action cannot validate its closure.
Quality check
Flags vague causes such as "human error", missing criteria, weak recommendations, and similar findings raised before.
Auditee dialogue
Auditees accept or dispute, comment with @mentions, and propose actions with dates. Everything stays on the finding.
Actions and proof
Corrective actions with owners and due dates. Auditees upload proof; the audit team validates before closing.
SLAs and escalation
Response and remediation targets by severity (for example 15 days for critical), automatic reminders and escalation when they are missed.
Extensions on the record
Owners request more time with a reason; a manager approves or refuses, and the decision is kept.
Follow-up without chasing.
Open actions, overdue items and pending validations appear on everyone's task list. Auditees get reminders before due dates, and managers see who is late before the committee asks.
See it with your own checklists.
Open the live demo now, or book a walkthrough and we will load one of your frameworks or work programmes.