Quality control for every change request.
Check each change against your standards before development starts, before testing, during test governance and before go-live, and stop non-compliances reaching production.
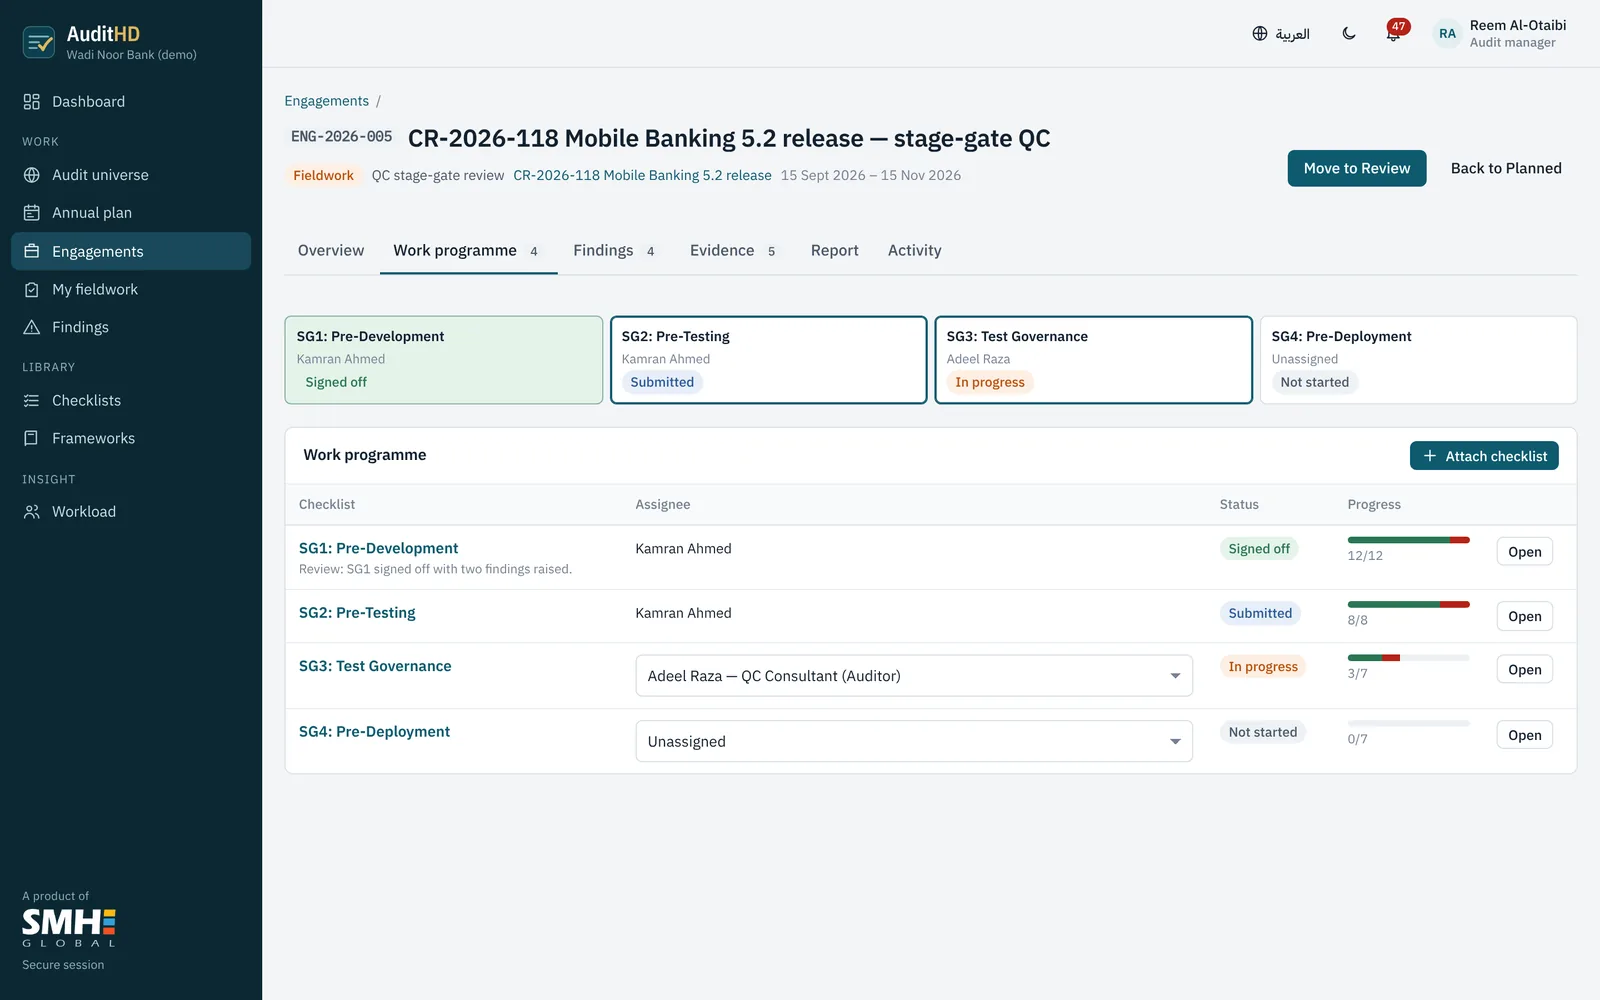
Four gates, 34 checks, ready to use.
The Change Request Stage-Gate QC template covers the checks QC teams run most, each linked to SAMA ITGF and CMMI references. Adapt it to your own standard.
1. Pre-development (12)
Approved scope and acceptance criteria, architecture approval, separated environments, secure coding standard, static analysis in the pipeline, security and privacy risk assessment.
2. Pre-testing (8)
Approved test plan, traceability to requirements, recorded peer review, clean code and dependency scans, masked test data, controlled deployment to test.
3. Test governance (7)
All test cycles run, no open critical defects unless formally accepted, security testing for internet-facing changes, performance, regression, UAT sign-off.
4. Pre-deployment (7)
CAB approval, a tested rollback plan, deployment by operations rather than developers, security sign-off, monitoring, and a post-implementation review.
Findings that reach the right person.
- Each gate goes to a different reviewer, and their load is visible before assignment.
- A failed check becomes a finding with its gate, clause and evidence already filled in.
- Dashboards show findings by stage gate, so recurring weaknesses are easy to see.
- The AI reviewer spots draft documents offered as approvals.
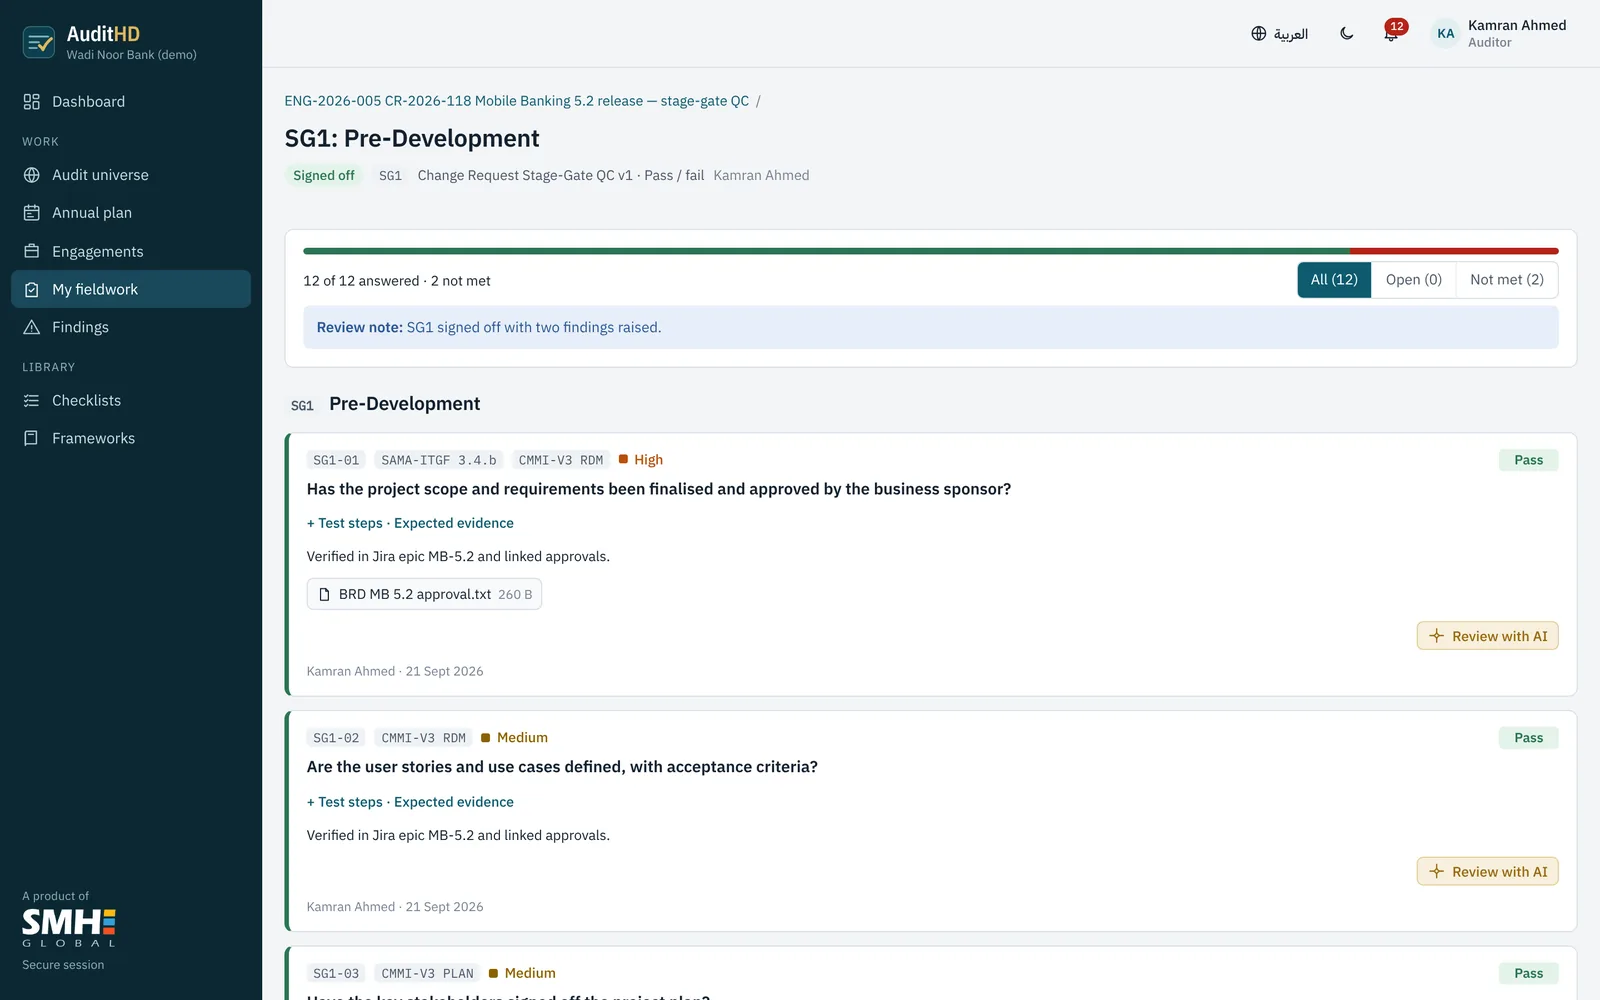
See it with your own checklists.
Open the live demo now, or book a walkthrough and we will load one of your frameworks or work programmes.