Everything an audit team does, from plan to closure.
AuditHD replaces the spreadsheets, shared folders and email chains that audit, QA and compliance teams run on today. Plan, test, raise findings, follow up and report in one system, with a complete record of who did what and when.
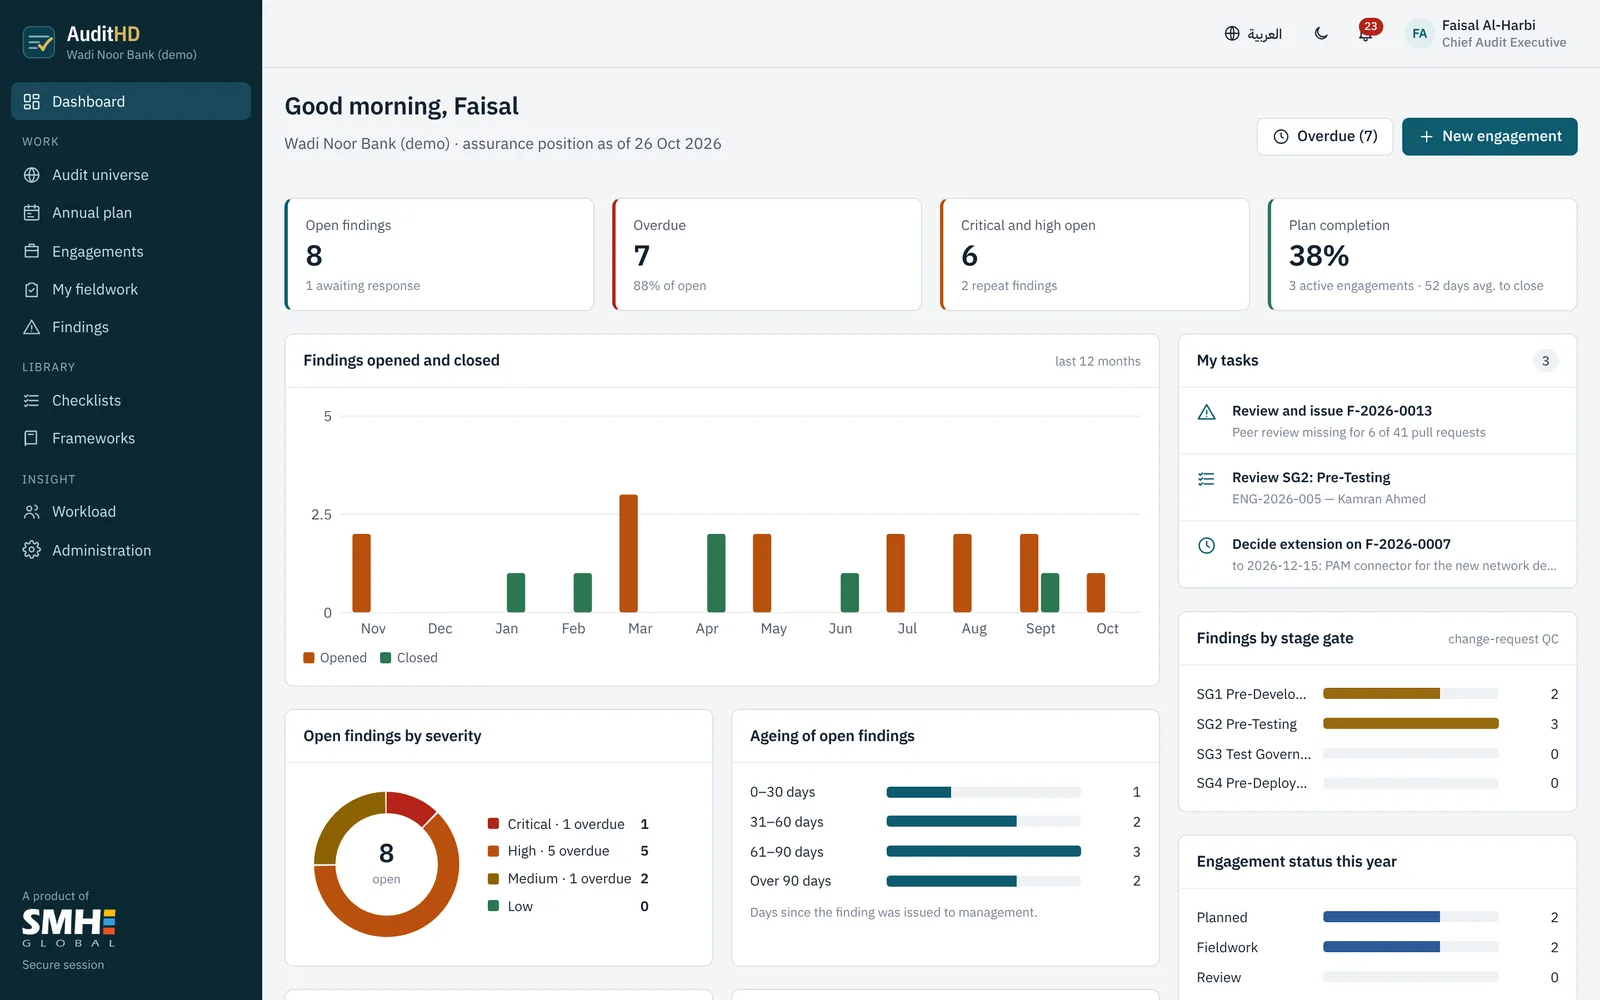
Five stages, one record.
Each stage passes its work to the next, so the plan, the tests, the findings and the follow-up stay connected.
1. Risk-based planning
Audit universe with likelihood, impact and control scores, a heat map, and an annual plan built from the highest risks.
2. Checklists and work programmes
Framework checklists out of the box, your own templates, CSV import, AI-drafted checklists, and assignment by stage gate.
3. Fieldwork and evidence
Pass, fail or maturity scoring, notes and evidence per item, photos with location, offline work and AI review before sign-off.
4. Findings and remediation
Findings in the 5C format, maker-checker review, auditee responses, action plans, extensions, SLAs and escalation.
5. Reporting and dashboards
Bilingual Word reports, Excel registers, committee dashboards, compliance index by unit, and recurring-issue analysis.
AI review throughout
Suggestions that cite the clause and the evidence, approved or discarded by a person, and logged either way.
Eight roles, each with the right view.
People see the work that belongs to them. Separation of duties is enforced by the system, not by goodwill.
| Role | Typically | What they do in AuditHD |
|---|---|---|
| Administrator | Audit systems owner | Users, departments, SLAs, branding, AI settings, licence, audit-trail verification |
| Chief audit executive | CAE, head of internal audit | Approves the plan, sees every engagement, reports to the audit committee |
| Manager | Audit manager, QC lead | Runs engagements, assigns checklists, reviews and issues findings, validates closure |
| Auditor | Auditor, QC consultant | Performs fieldwork, attaches evidence, drafts findings |
| Quality reviewer | QA reviewer | Reviews workpapers and findings before they go out |
| Risk and control officer | Operational risk, compliance (second line) | Runs the quarterly RCSA, challenges or signs off each unit's self-assessment, raises issues |
| Auditee | Business and IT owners | Sees only findings for their unit; responds, plans actions, uploads proof; keeps the unit's risks, controls and self-assessment tests |
| Viewer | Audit committee, regulators on request | Read-only dashboards and reports |
Maker-checker rules: the person who raised a finding cannot issue it, and the owner of a corrective action cannot close it.
See it with your own checklists.
Open the live demo now, or book a walkthrough and we will load one of your frameworks or work programmes.