Ready-made country packs.
Every country sets its own rules for banks, lenders, listed companies and large enterprises. A country pack loads them into AuditHD: the regulators' frameworks, checklists ready to run, the calendar of regulatory deadlines, record-retention periods and rating rules. License the countries you work in. International standards come with every licence.
Gulf Cooperation Council
Saudi Arabia
SAMA, the National Cybersecurity Authority, the Capital Market Authority, SDAIA (PDPL) and ZATCA.
SAMANCASDAIACMAZATCA 15 frameworks · 8 checklists · 20 deadlines AEUnited Arab Emirates
Central Bank of the UAE, the Securities and Commodities Authority, UAE data protection and AML law.
CBUAEHSAFIUSCAUAEDOTDRA 11 frameworks · 5 checklists · 20 deadlines BHBahrain
Central Bank of Bahrain Rulebook, Shari'a governance and Bahrain's personal data protection law.
CBBMOICPDPA 8 frameworks · 4 checklists · 20 deadlines QAQatar
Qatar Central Bank, the Qatar Financial Markets Authority, national information assurance and data privacy.
QCBQFMANCSAQFCRA 7 frameworks · 4 checklists · 16 deadlines KWKuwait
Central Bank of Kuwait (including cyber and operational resilience), the Capital Markets Authority and the internal control review.
CBKCMAKFIUCITRANCSCMOCI 9 frameworks · 4 checklists · 19 deadlines OMOman
Central Bank of Oman, the Financial Services Authority, Islamic banking and Oman's personal data protection law.
CBOFSANCFIMTCIT 7 frameworks · 4 checklists · 13 deadlinesSouth Asia, Europe and the Americas
Pakistan
State Bank of Pakistan, SECP, State-Owned Enterprises Act and Shariah governance.
SBPSECPFD-CMU 13 frameworks · 5 checklists · 20 deadlines EUEuropean Union
GDPR, DORA, NIS2, the AI Act, the AML Regulation, EBA guidelines and sustainability reporting.
ECEBAESMAEIOPAECB-SSMAMLA 10 frameworks · 5 checklists · 20 deadlines USUnited States
Sarbanes-Oxley, FDIC Part 363, OCC Heightened Standards, FFIEC, GLBA, BSA/AML and OFAC, NYDFS Part 500, SEC cyber disclosure and CCPA.
SECPCAOBFRBOCCFDICFinCEN 11 frameworks · 5 checklists · 20 deadlinesIncluded with every licence
Inside AuditHD.
Library → Country packs shows every pack, what your organisation has licensed and what each pack holds. Open a pack for its regulators, frameworks, checklists, regulatory calendar and retention rules, and apply its reporting conventions to your rating methodology in one step.
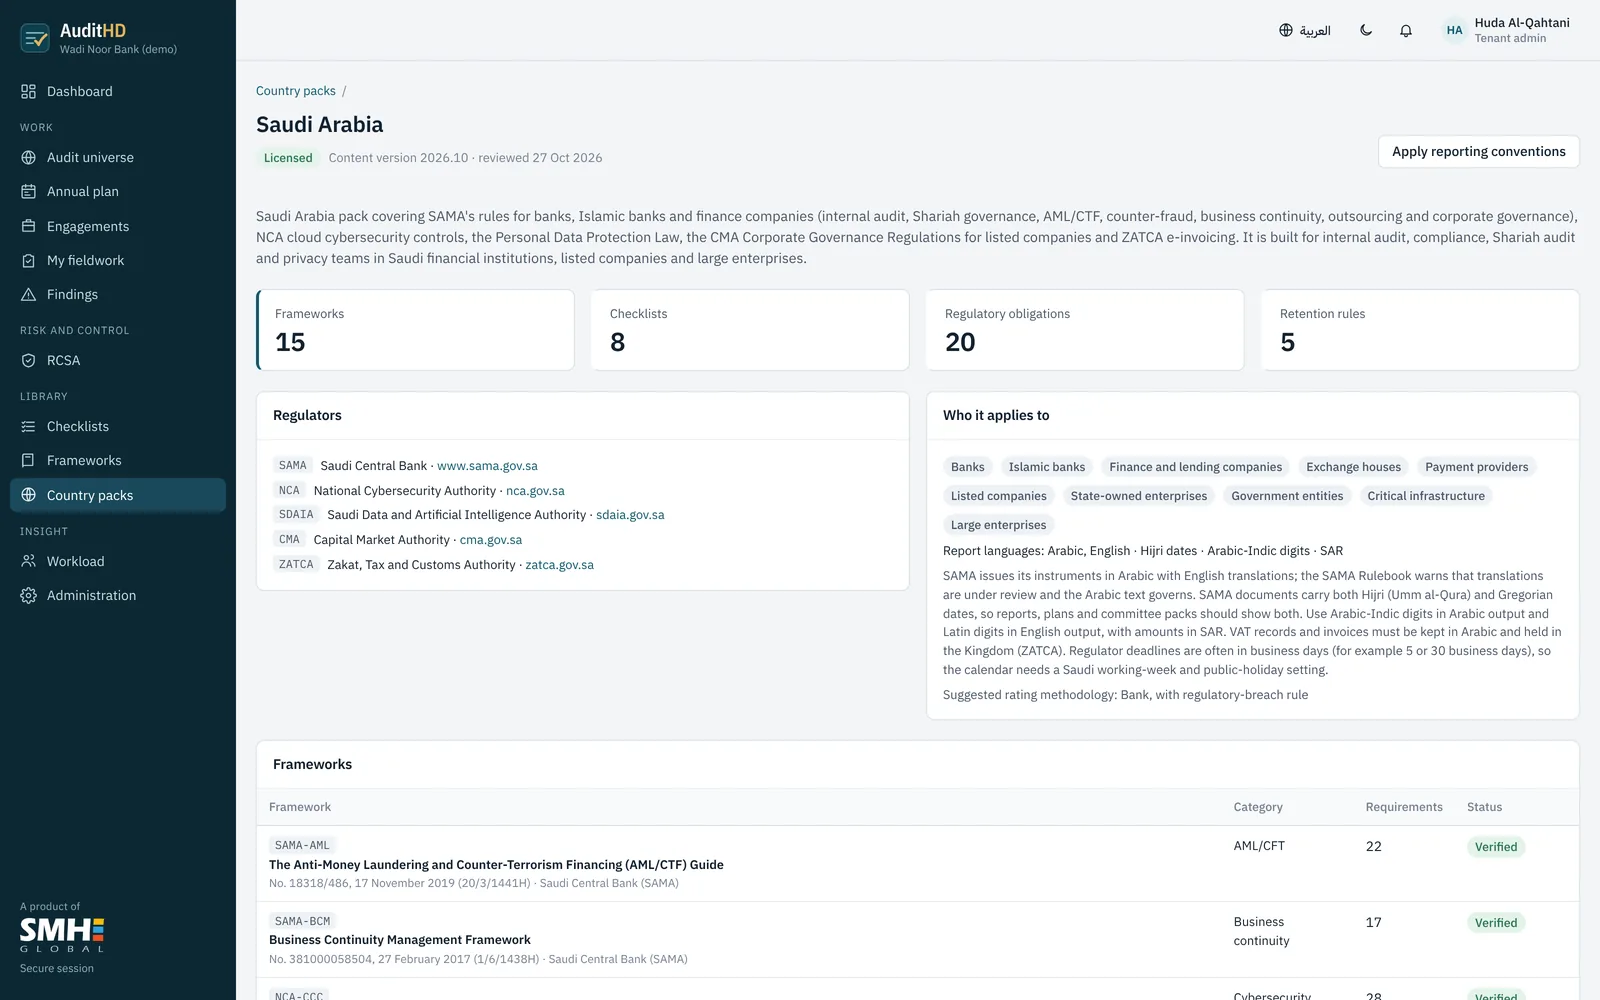
What is in a pack.
The same six parts for every country, so a group that operates in several countries works the same way everywhere.
Frameworks and regulations
Each regulator's instruments, with their own article and section numbers where confirmed, a plain-language description of every requirement and a link to the official text.
Checklists ready to run
Audit programmes built on those requirements: internal audit function reviews, AML/CFT independent testing, Shariah compliance audits, ICFR, cyber, data protection and governance reviews.
Regulatory calendar
The recurring deliverables: annual opinions, committee reports, independent reviews, external quality assessments, certifications and incident-notice deadlines, with who requires them.
Record retention
How long AML records, audit working papers and other records must be kept under each regime, so retention settings match the strictest rule that applies.
Rating rules and conventions
Regulators' rules on rating findings, such as SAMA's default high rating for breaches of its instructions, and reporting conventions: Arabic, Urdu, Hijri dates and Arabic-Indic digits.
Kept current
Each pack carries a content version and review date. Items checked against the regulator's own publication are marked, and updates arrive with your subscription or maintenance.
Who the packs cover.
- Banks and Islamic banks: governance, internal audit, compliance, operational risk, AML/CFT, cyber, outsourcing, business continuity and Shariah governance.
- Lenders and other financial institutions: finance companies, microfinance banks, NBFCs, insurers, payment providers and exchange houses.
- Listed companies: corporate governance codes, audit committees and internal control over financial reporting.
- State-owned and large enterprises: data protection, national cybersecurity rules, anti-bribery and e-invoicing.
How licensing works.
- International standards (ISO, COSO, PCI DSS, NIST, FATF and more) are included with every licence.
- License one country pack or several. A group with operations across the GCC, Pakistan, Europe or the US licenses each country it reports to.
- Packs you have not licensed stay visible in the library, locked, so you can see what they contain.
- On-premises and air-gapped licences list the packs inside the signed licence file, so nothing needs to call home.
Regulator text and verification.
AuditHD does not reproduce regulators' or standard-setters' wording. Requirements are identified by their official numbers and titles and described in our own words, with a link to the official text. Organisations that hold a licence for the official wording of a standard can load it into their own private copy.
Regulations change. Every framework, deadline and retention rule in a pack shows whether it has been checked against the regulator's own publication, and each pack lists what is still being confirmed. Content version 2026.10, reviewed 27 October 2026.
See it with your own checklists.
Open the live demo now, or book a walkthrough and we will load one of your frameworks or work programmes.