
Packs
Ready-made packs for your country, your industry and your export markets.
Pick your industry — banking, insurance, textiles and apparel, food and beverages, manufacturing, the public sector — and AuditHD puts the right content first. Country packs load one jurisdiction's regulators; industry packs load the standards, buyer codes and domestic rules of your sector; market-access packs load what an exporter must meet to sell into the EU, the UK, the United States or the Gulf. Each pack brings frameworks, checklists ready to run, a calendar of deadlines, record-retention periods and rating rules. International standards come with every licence.
Industry packs — for manufacturers and exporters
TEX · industry pack
Textiles and apparel
Social compliance (amfori BSCI, Sedex SMETA, WRAP, SA8000, Higg FSLM), chemicals and product safety (OEKO-TEX, ZDHC, GOTS, GRS), environment, Pakistan labour and factory rules and supply-chain security (C-TPAT).
- amfori
- Sedex
- WRAP
- SAI
- Cascale
- OEKO-TEX
13 frameworks · 4 checklists · 15 deadlines
FNB · industry pack
Food and beverages
Food safety (Codex HACCP, ISO 22000, FSSC 22000, BRCGS, IFS Food, SQF), halal (PS 3733, SMIIC, GSO 2055), Pakistan food authorities and PSQCA, traceability and recall, allergens and labelling.
- Codex
- GFSI
- FSSC
- BRCGS
- IFS
- SQFI
9 frameworks · 4 checklists · 14 deadlines
Market-access packs — what importing countries require
XEU · market-access pack
EU market access
What an exporter to the European Union must meet: REACH and chemicals, GSP+ conventions, the Deforestation Regulation, CSDDD and buyer due-diligence questionnaires, German LkSG, EU food hygiene, labelling and import controls, textile labelling and ecodesign.
- EC
- ECHA
- EFSA
- BAFA
- Customs
10 frameworks · 3 checklists · 12 deadlines
XUK · market-access pack
UK market access
What an exporter to the United Kingdom must meet: Modern Slavery Act statements, UK REACH, the Developing Countries Trading Scheme, FSA import rules, food labelling and allergens, product safety and textile labelling.
- DBT
- HMRC
- FSA
- HSE
- OPSS
- Home Office
7 frameworks · 3 checklists · 9 deadlines
XUS · market-access pack
US market access
What an exporter to the United States must meet: FDA FSMA (foreign supplier verification, preventive controls, facility registration), the Uyghur Forced Labor Prevention Act and CBP forced-labour enforcement, C-TPAT, CPSC apparel safety and FTC textile labelling.
- FDA
- CBP
- CPSC
- FTC
- USDA
- FLETF
7 frameworks · 3 checklists · 10 deadlines
XGC · market-access pack
GCC market access
What an exporter to the Gulf states must meet: GSO halal and food standards, SFDA food import and labelling rules, SASO and SABER conformity, ESMA and MoIAT conformity marks, and the GCC conformity mark.
- GSO
- GAC
- SFDA
- SASO
- ZATCA
- MoIAT
6 frameworks · 3 checklists · 10 deadlines
Country packs — Gulf Cooperation Council
SA · country pack
Saudi Arabia
SAMA, the National Cybersecurity Authority, the Capital Market Authority, SDAIA (PDPL) and ZATCA.
- SAMA
- NCA
- SDAIA
- CMA
- ZATCA
15 frameworks · 8 checklists · 20 deadlines
AE · country pack
United Arab Emirates
Central Bank of the UAE, the Securities and Commodities Authority, UAE data protection and AML law.
- CBUAE
- HSA
- FIU
- SCA
- UAEDO
- TDRA
11 frameworks · 5 checklists · 20 deadlines
BH · country pack
Bahrain
Central Bank of Bahrain Rulebook, Shari'a governance and Bahrain's personal data protection law.
- CBB
- MOIC
- PDPA
8 frameworks · 4 checklists · 20 deadlines
QA · country pack
Qatar
Qatar Central Bank, the Qatar Financial Markets Authority, national information assurance and data privacy.
- QCB
- QFMA
- NCSA
- QFCRA
7 frameworks · 4 checklists · 16 deadlines
KW · country pack
Kuwait
Central Bank of Kuwait (including cyber and operational resilience), the Capital Markets Authority and the internal control review.
- CBK
- CMA
- KFIU
- CITRA
- NCSC
- MOCI
9 frameworks · 4 checklists · 19 deadlines
OM · country pack
Oman
Central Bank of Oman, the Financial Services Authority, Islamic banking and Oman's personal data protection law.
- CBO
- FSA
- NCFI
- MTCIT
7 frameworks · 4 checklists · 13 deadlines
Country packs — South Asia, Europe and the Americas
PK · country pack
Pakistan
State Bank of Pakistan, SECP, State-Owned Enterprises Act and Shariah governance.
- SBP
- SECP
- FD-CMU
13 frameworks · 5 checklists · 20 deadlines
BD · country pack
Bangladesh
Bangladesh Bank (internal control, cybersecurity, ICT security, Shariah), BFIU AML/CFT, BSEC corporate governance, finance companies and microfinance, and the 2026 data protection and cyber security laws.
- BB
- BFIU
- BSEC
- IDRA
- MRA
- FRC
10 frameworks · 5 checklists · 20 deadlines
EU · country pack
European Union
GDPR, DORA, NIS2, the AI Act, the AML Regulation, EBA guidelines and sustainability reporting.
- EC
- EBA
- ESMA
- EIOPA
- ECB-SSM
- AMLA
10 frameworks · 5 checklists · 20 deadlines
US · country pack
United States
Sarbanes-Oxley, FDIC Part 363, OCC Heightened Standards, FFIEC, GLBA, BSA/AML and OFAC, NYDFS Part 500, SEC cyber disclosure and CCPA.
- SEC
- PCAOB
- FRB
- OCC
- FDIC
- FinCEN
11 frameworks · 5 checklists · 20 deadlines
Included with every licence
Inside AuditHD.
Set your organisation's industry once, and Library → Packs shows the packs and frameworks that apply to it first, what your organisation has licensed and what each pack holds. Open a pack for its regulators, frameworks, checklists, regulatory calendar and retention rules, and apply its reporting conventions to your rating methodology in one step.
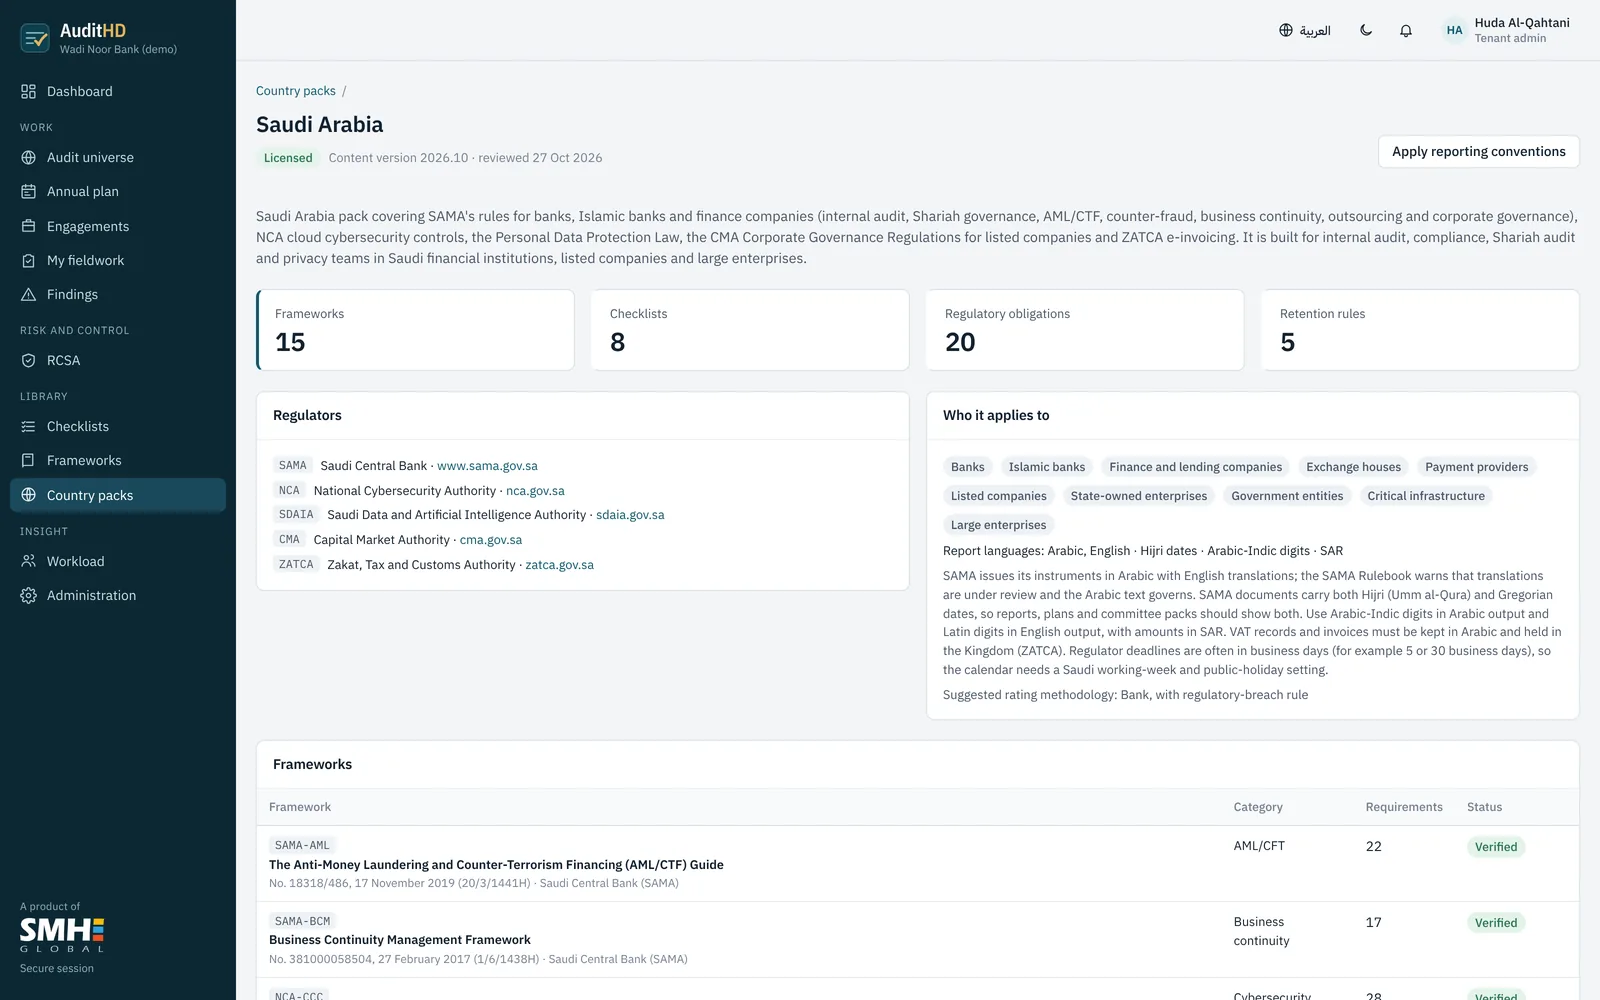
What is in a pack.
The same six parts in every pack, so a group that operates in several countries or sells into several markets works the same way everywhere.
Frameworks and regulations
Each regulator's instruments, with their own article and section numbers where confirmed, a plain-language description of every requirement and a link to the official text.
Checklists ready to run
Audit programmes built on those requirements: internal audit function reviews, AML/CFT independent testing, Shariah compliance audits, ICFR, cyber, data protection and governance reviews.
Regulatory calendar
The recurring deliverables: annual opinions, committee reports, independent reviews, external quality assessments, certifications and incident-notice deadlines, with who requires them.
Record retention
How long AML records, audit working papers and other records must be kept under each regime, so retention settings match the strictest rule that applies.
Rating rules and conventions
Regulators' rules on rating findings, such as SAMA's default high rating for breaches of its instructions, and reporting conventions: Arabic, Urdu, Hijri dates and Arabic-Indic digits.
Kept current
Each pack carries a content version and review date. Items checked against the regulator's own publication are marked, and updates arrive with your subscription or maintenance.
Who the packs cover.
- Banks and Islamic banks: governance, internal audit, compliance, operational risk, AML/CFT, cyber, outsourcing, business continuity and Shariah governance.
- Lenders and other financial institutions: finance companies, microfinance banks, NBFCs, insurers, payment providers and exchange houses.
- Listed companies: corporate governance codes, audit committees and internal control over financial reporting.
- State-owned and large enterprises: data protection, national cybersecurity rules, anti-bribery and e-invoicing.
- Textile, apparel and leather exporters: the social compliance audits buyers demand (amfori BSCI, Sedex SMETA, WRAP, SA8000, Higg), chemicals and product safety (OEKO-TEX, ZDHC, GOTS, GRS), environment and the Pakistani labour and factory rules those audits test.
- Food and beverage manufacturers: Codex HACCP, ISO 22000, FSSC 22000, BRCGS, IFS, SQF, halal, provincial food-authority licensing, traceability, recall and allergens.
- Exporters to the EU, the UK, the United States and the GCC: REACH, GSP+ and DCTS origin, the Deforestation and Forced Labour regulations, CSDDD and LkSG questionnaires, FSMA, UFLPA, CPSC and FTC rules, SFDA, SABER, GSO and halal recognition.
- Audit and consulting firms: every pack, for every client industry.
How licensing works.
- International standards (ISO, COSO, PCI DSS, NIST, FATF and more) are included with every licence.
- License one country pack or several. A group with operations across the GCC, South Asia, Europe or the US licenses each country it reports to.
- Packs you have not licensed stay visible in the library, locked, so you can see what they contain.
- On-premises and air-gapped licences list the packs inside the signed licence file, so nothing needs to call home.
Regulator text and verification.
AuditHD does not reproduce regulators' or standard-setters' wording. Requirements are identified by their official numbers and titles and described in our own words, with a link to the official text. Organisations that hold a licence for the official wording of a standard can load it into their own private copy.
Regulations change. Every framework, deadline and retention rule in a pack shows whether it has been checked against the regulator's own publication, and each pack lists what is still being confirmed. Content version 2026.10, reviewed 27 October 2026.
See it with your own checklists.
Open the live demo now, or book a walkthrough and we will load one of your frameworks or work programmes.