
Framework library
The frameworks your auditors work to, already loaded.
These are the frameworks described in detail below. The full library has more than a hundred frameworks and regulations, organised into country packs for Pakistan, Bangladesh, the GCC, the EU and the US. Checklist items, findings and reports all point to the exact clause.
Frameworks in the library
Saudi Central Bank (SAMA)
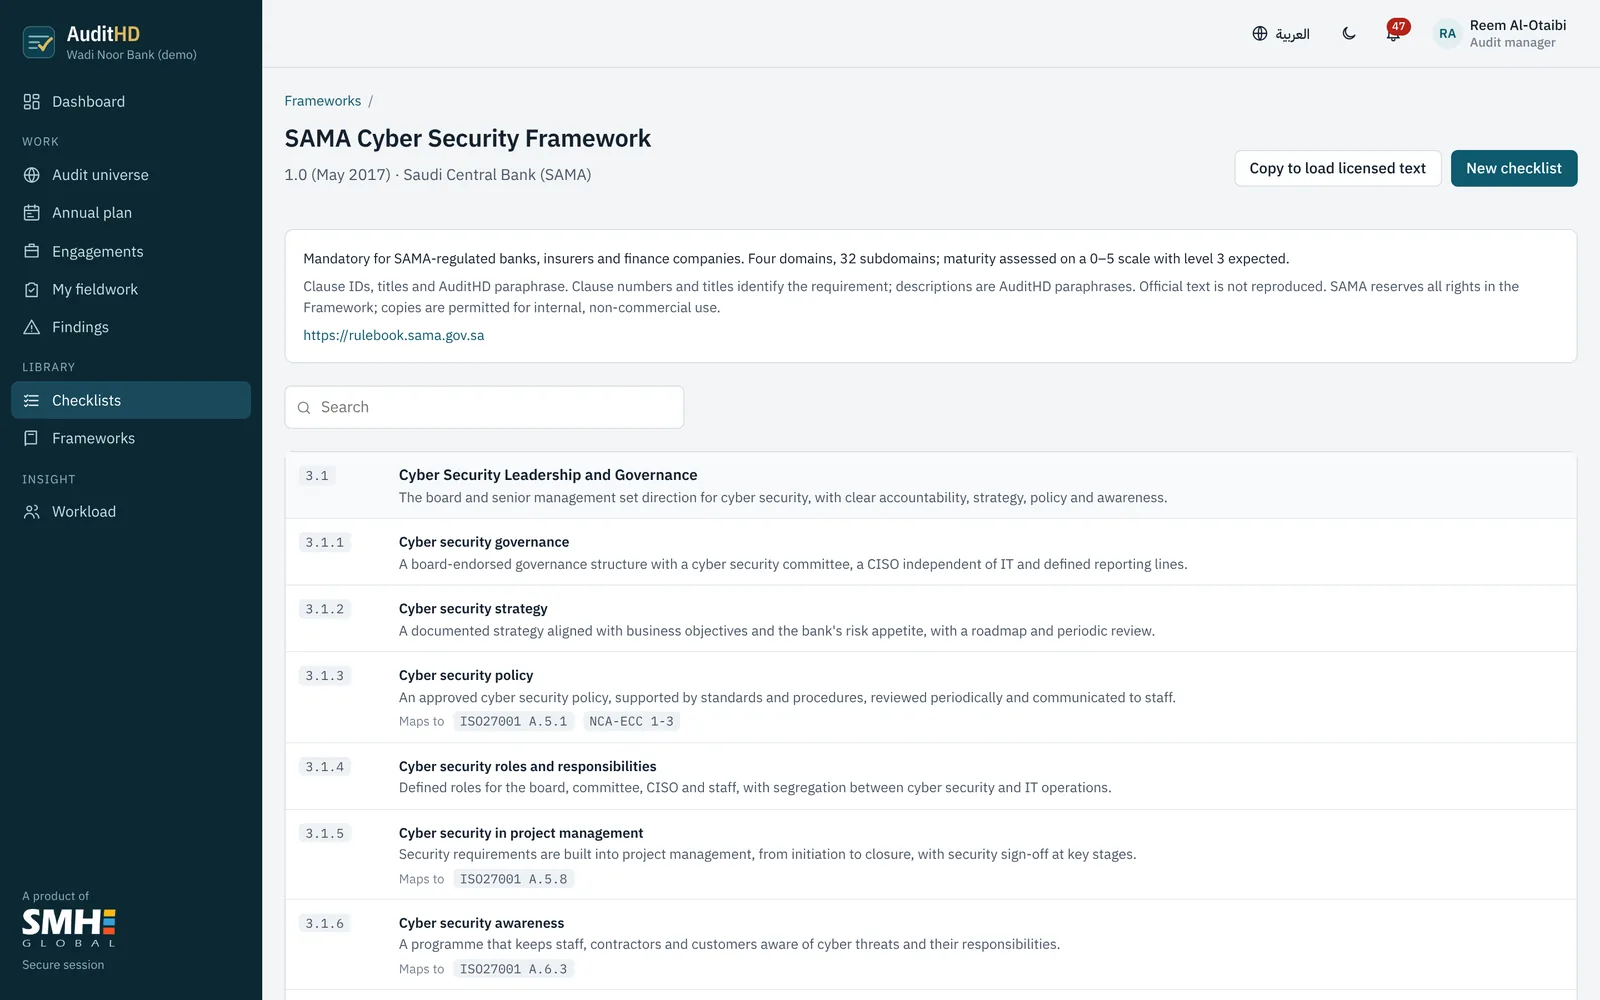
SAMA Cyber Security Framework
Banks, insurers, finance companies and other organisations regulated by SAMA.
- 1.0 (May 2017)
- Saudi Arabia
Saudi Central Bank (SAMA)
SAMA IT Governance Framework
SAMA-regulated organisations.
- 1.0 (2021)
- Saudi Arabia
National Cybersecurity Authority (Saudi Arabia)
NCA Essential Cybersecurity Controls
Government organisations and private-sector organisations that own, operate or host critical national infrastructure.
- ECC-2:2024
- Saudi Arabia
ISO/IEC
ISO/IEC 27001 Information security management systems
Any organisation running or certifying an information security management system.
- 2022 + Amd 1:2024
- International
ISO
ISO 9001 Quality management systems
Organisations running or certifying a quality management system, including banks' operations and service functions.
- 2015
- International
ISACA / CMMI Institute
CMMI Model: development and security views
Software and IT organisations improving delivery capability, and the consultancies that appraise them.
- V3.0
- International
U.S. National Institute of Standards and Technology
NIST Cybersecurity Framework
Organisations of any size; widely referenced by US financial regulators and used as a common language internationally.
- 2.0 (February 2024)
- United States and international
State Bank of Pakistan
SBP Enterprise Technology Governance and Risk Management Framework
Banks and development finance institutions in Pakistan.
- BPRD Circular 05/2017
- Pakistan
Map once, test once.
Many controls appear in several frameworks. AuditHD links them, so one test can serve a SAMA CSF assessment, an ISO 27001 internal audit and an NCA ECC review.
- 51 links between SAMA CSF, NCA ECC, ISO/IEC 27001 and NIST CSF
- See every related requirement from any clause
- Findings cite all the requirements they affect
Your own policies count too.
Internal policies, procedures and client-specific standards become checklists in the same way, so a policy-compliance review looks and reports like any other audit.
Respecting copyright.
Clause numbers and titles identify each requirement; descriptions are our own plain-language summaries. Official wording is not reproduced, and organisations that hold a licence can load it privately. NIST content is in the public domain and included in full.
See it with your own checklists.
Open the live demo now, or book a walkthrough and we will load one of your frameworks or work programmes.